UK Financial Regulators Propose Cyber Guidance as Incident Reports Hit 18-Month High

Thursday, 19/11/2026 | 10:06 GMT by Damian Chmiel
  • October's count was the second-highest in five years and 52% above the previous high, recorded in May 2025.
  • The draft adds no new rules, and comments close in February 2027, eight months before crypto firms come into scope.
cyber

Cyber incidents reported to the Financial Conduct Authority (FCA) hit an 18-month high in October, the regulator said today (Thursday) as it proposed cyber guidance. The October count was the second-highest in five years and 52% above the previous high, recorded in May 2025.

The FCA drafted the guidance jointly with the Prudential Regulation Authority (PRA) and the Bank of England. Firms, trade associations and technology providers can comment until February 26, 2027.

Outside suppliers have been a recurring source of incidents. More than 40% of cyber incidents reported to the FCA in 2025 involved a third party, a figure the regulator gave when it confirmed new incident-reporting rules covering CFD brokers in March. Those rules apply from March 18, 2027.

London's trading industry is coming home!

Guidance Instead of New Rules

The draft, published as consultation GC26/9, gathers existing requirements and lessons from supervision into one text. It follows the National Cyber Security Centre's (NCSC) Cyber Assessment Framework.

It covers five areas: governance, mapping critical systems and their dependencies, protection, detection, and response and recovery.
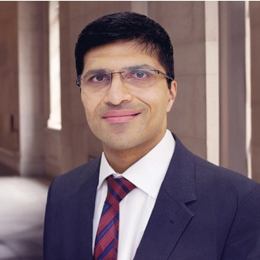
Nikhil Rathi, Chief Executive of the FCA, Source: Bank of England

"Our response shouldn't always be more rules," FCA Chief Executive Nikhil Rathi said. Firms had asked the regulator for clarity on what good cyber resilience looks like, he added.

Rathi took a similar line on artificial intelligence in October, when he said the FCA would make full use of its existing powers before asking for new ones. The cyber draft follows the same approach, and the regulators said it gives firms flexibility in how they meet the expectations.

Suppliers, AI and Quantum Computing

Under the protection heading, the draft asks firms to apply controls over third parties and supply chains, alongside secure configuration, patching, access management and data protection.

A breach in Japan in October showed how such dependencies can reach client accounts. Five Japanese FX brokers confirmed that hackers placed trades on client accounts after attackers got into a rented server service run by GMO Internet Group. GMO said up to 26,739 servers may have been exposed.

Alongside the consultation, the regulators published separate effective practices on threats from AI and on quantum computing, which could weaken the public-key cryptography behind financial transactions.

Those papers are not open for formal consultation, though the regulators asked firms whether such material is useful.

In a recent Bank of England and FCA survey, 88% of respondents said frontier AI cyber capabilities would have a moderate or high impact on their risk profile over the next two years. Patching and vulnerability management drew the biggest increase in management attention, cited by 64%.

Supervisors outside the UK have published on the same risk. FM Intelligence's regulation tracker logged 24 cyber-related publications by financial regulators in 2026 through November 13, from Australia, Germany, the European Union, the United Arab Emirates and international bodies.

Which Firms Fall Within Scope

The guidance applies to firms already covered by the regulators' operational resilience requirements, including banks, building societies, Solvency II insurers and recognized investment exchanges.

Electronic money and payment institutions are in scope, as are enhanced-scope firms under the Senior Managers and Certification Regime (SM&CR). Qualifying cryptoasset firms join from October 25, 2027.

Other FCA solo-regulated firms and UK branches of non-UK firms fall outside it, though the FCA encourages them to read it.

For retail brokers, the line runs through the enhanced tier of SM&CR. The FCA says that tier applies to "a small number of firms", including CASS large firms, those holding the most client money.

In March, FM Intelligence counted 23 FCA-regulated brokers with $9.3 trillion in combined monthly volumes facing direct exposure to the regulator's widening compliance demands.

The FCA expects to publish the final guidance in the first half of 2027, after the consultation closes.

Cyber incidents reported to the Financial Conduct Authority (FCA) hit an 18-month high in October, the regulator said today (Thursday) as it proposed cyber guidance. The October count was the second-highest in five years and 52% above the previous high, recorded in May 2025.

The FCA drafted the guidance jointly with the Prudential Regulation Authority (PRA) and the Bank of England. Firms, trade associations and technology providers can comment until February 26, 2027.

Outside suppliers have been a recurring source of incidents. More than 40% of cyber incidents reported to the FCA in 2025 involved a third party, a figure the regulator gave when it confirmed new incident-reporting rules covering CFD brokers in March. Those rules apply from March 18, 2027.

London's trading industry is coming home!

Guidance Instead of New Rules

The draft, published as consultation GC26/9, gathers existing requirements and lessons from supervision into one text. It follows the National Cyber Security Centre's (NCSC) Cyber Assessment Framework.

It covers five areas: governance, mapping critical systems and their dependencies, protection, detection, and response and recovery.

Nikhil Rathi, Chief Executive of the FCA, Source: Bank of England

"Our response shouldn't always be more rules," FCA Chief Executive Nikhil Rathi said. Firms had asked the regulator for clarity on what good cyber resilience looks like, he added.

Rathi took a similar line on artificial intelligence in October, when he said the FCA would make full use of its existing powers before asking for new ones. The cyber draft follows the same approach, and the regulators said it gives firms flexibility in how they meet the expectations.

Suppliers, AI and Quantum Computing

Under the protection heading, the draft asks firms to apply controls over third parties and supply chains, alongside secure configuration, patching, access management and data protection.

A breach in Japan in October showed how such dependencies can reach client accounts. Five Japanese FX brokers confirmed that hackers placed trades on client accounts after attackers got into a rented server service run by GMO Internet Group. GMO said up to 26,739 servers may have been exposed.

Alongside the consultation, the regulators published separate effective practices on threats from AI and on quantum computing, which could weaken the public-key cryptography behind financial transactions.

Those papers are not open for formal consultation, though the regulators asked firms whether such material is useful.

In a recent Bank of England and FCA survey, 88% of respondents said frontier AI cyber capabilities would have a moderate or high impact on their risk profile over the next two years. Patching and vulnerability management drew the biggest increase in management attention, cited by 64%.

Supervisors outside the UK have published on the same risk. FM Intelligence's regulation tracker logged 24 cyber-related publications by financial regulators in 2026 through November 13, from Australia, Germany, the European Union, the United Arab Emirates and international bodies.

Which Firms Fall Within Scope

The guidance applies to firms already covered by the regulators' operational resilience requirements, including banks, building societies, Solvency II insurers and recognized investment exchanges.

Electronic money and payment institutions are in scope, as are enhanced-scope firms under the Senior Managers and Certification Regime (SM&CR). Qualifying cryptoasset firms join from October 25, 2027.

Other FCA solo-regulated firms and UK branches of non-UK firms fall outside it, though the FCA encourages them to read it.

For retail brokers, the line runs through the enhanced tier of SM&CR. The FCA says that tier applies to "a small number of firms", including CASS large firms, those holding the most client money.

In March, FM Intelligence counted 23 FCA-regulated brokers with $9.3 trillion in combined monthly volumes facing direct exposure to the regulator's widening compliance demands.

The FCA expects to publish the final guidance in the first half of 2027, after the consultation closes.

About the Author: Damian Chmiel
Damian Chmiel
  • 4212 Articles
  • 120 Followers
About the Author: Damian Chmiel
Damian Chmiel is a Senior Analyst & Editor at Finance Magnates with more than 15 years of experience in the CFD and online trading industry. Active as both a trader and journalist since 2010, he focuses on broker coverage, fintech innovation, and regulatory developments across Europe, the Middle East, and Asia. His work includes interviews with C-level leaders at major brokerages and fintech platforms, as well as co-authoring Finance Magnates’ quarterly industry benchmarking reports. Damian’s reporting is data-driven, market-aware, and grounded in direct industry engagement. His analysis and commentary have also been cited by external media outlets, including Investing.com, Binance, The Asset, Stockhead, and Dispatch. Education: MA in Finance and Accounting, Cracow University of Economics
  • 4212 Articles
  • 120 Followers

More from the Author

Retail FX

!"#$%&'()*+,-./0123456789:;<=>?@ABCDEFGHIJKLMNOPQRSTUVWXYZ[\]^_`abcdefghijklmnopqrstuvwxyz{|} !"#$%&'()*+,-./0123456789:;<=>?@ABCDEFGHIJKLMNOPQRSTUVWXYZ[\]^_`abcdefghijklmnopqrstuvwxyz{|}